Social media websites depend on secure user accounts, messaging systems, profile pages, media uploads, and administrative dashboards. When these features run on PHP, security weaknesses in the PHP runtime, application code, frameworks, or third-party libraries can expose sensitive information and put website operations at risk.
The importance of PHP security became especially clear on October 21, 2026, when the PHP development team released security updates addressing two critical vulnerabilities that could allow unauthenticated remote code execution. The official advisories identify the issues as CVE-2026-109618 and CVE-2026-109619.

For website owners, developers, and digital marketing teams, this is a reminder that website security requires more than strong passwords or an SSL certificate. It also requires timely software updates, secure coding practices, careful access controls, and continuous monitoring.
This guide explains how PHP vulnerabilities in social media websites can create security risks, what recent advisories reveal, how to recognize warning signs, and what steps businesses can take to protect their websites and user data.
What Is a PHP Vulnerability?
A PHP vulnerability is a security weakness in the PHP programming language, its runtime, or software built around it that could be exploited to affect a website or server.
PHP is a server-side programming language. It processes requests, interacts with databases, manages application logic, and generates dynamic web content. Many content management systems and web applications use PHP to provide interactive features.
A vulnerability may exist in several places:
PHP itself: A flaw in the language runtime could affect applications running vulnerable versions.
Application code: A developer may handle user input or database queries insecurely.
Frameworks and plugins: Outdated dependencies may contain known security weaknesses.
Server configuration: Excessive permissions or unsafe settings may increase the impact of a compromise.
For example, imagine a social networking website that allows members to upload profile pictures. If its upload process does not properly validate files and the server is configured unsafely, an attacker may be able to upload content that creates a security risk.
This is an illustrative scenario, not a claim about a particular website being hacked.
Importantly, not every PHP website is vulnerable. Risk depends on the software version, application design, configuration, exposure, and security controls.
How PHP Vulnerabilities in Social Media Websites Create Risks
Social media platforms handle personal information and user-generated content, making security failures potentially costly.
What should website owners do? Identify every PHP installation serving web requests, including installations managed by hosting providers or bundled with other software. Apply the appropriate patched release after checking application compatibility and deployment requirements.
The PHP team stated that updating was the only complete fix for these vulnerabilities. If an exposed system cannot be patched promptly, consult the hosting provider or security team about isolating it until remediation is possible.
These advisories describe a serious, confirmed vulnerability disclosure and available fixes. They do not, by themselves, prove that a specific social media website was successfully hacked or that every affected server has been exploited.
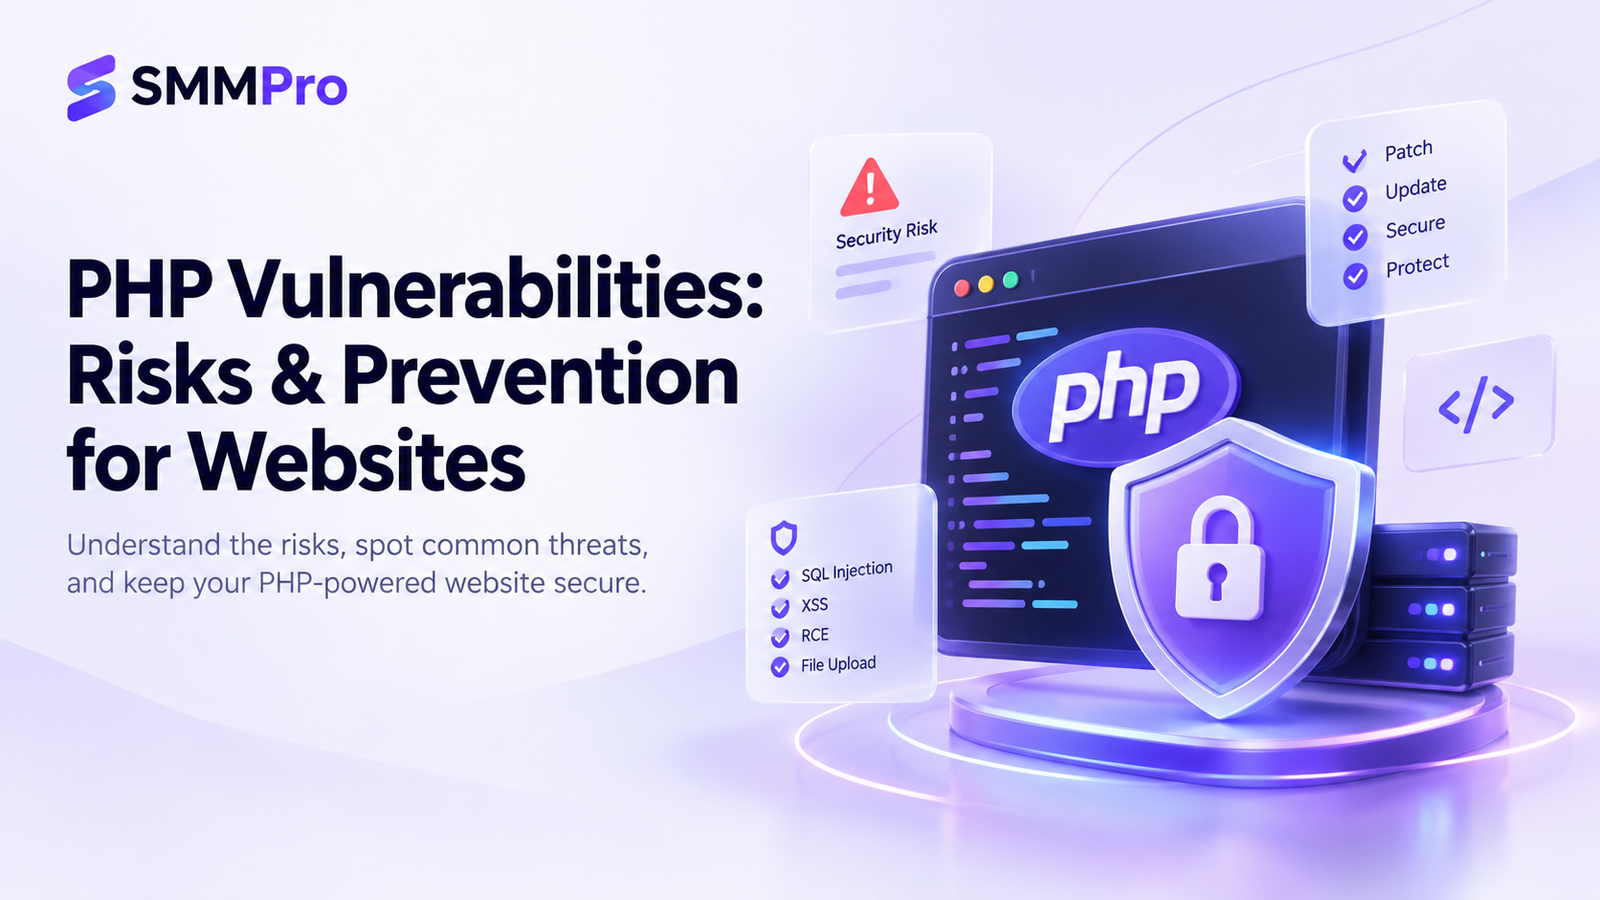
Common PHP Vulnerabilities Website Owners Should Know About
Not every web application security issue originates in PHP itself. Many arise from application logic, third-party packages, or server configuration.
1. SQL injection
SQL injection occurs when an application combines untrusted input with database commands unsafely. An attacker may be able to read or change information that the database account can access.
Prevention: Use prepared statements and parameterized queries, validate inputs, and limit database permissions.
2. Cross-site scripting (XSS)
Cross-site scripting happens when an application displays untrusted content in a way that allows a browser to interpret it as executable code. On a social platform, this could affect profile pages, comments, or shared posts.
Prevention: Apply context-appropriate output encoding, sanitize permitted user-authored HTML, and use modern framework protections correctly. Security headers such as Content Security Policy provide an additional layer, not a replacement for fixing the underlying flaw.
3. Remote code execution (RCE)
Remote code execution allows an attacker to execute code on a vulnerable system from a remote location. Depending on the vulnerability and the permissions of the affected process, the consequences can include data exposure, unauthorized changes, or server compromise.
Prevention: Install security patches promptly, minimize service permissions, and monitor exposed systems for suspicious activity.
4. PHP file upload vulnerabilities
Profile pictures, videos, and attachments create opportunities for unsafe file handling. Risks include accepting executable files, trusting misleading file extensions, and storing uploads in locations where the server may execute them.
Prevention: Allow only necessary file types, validate actual file content, enforce size limits, generate safe filenames, and store uploads outside executable web directories where practical.
5. Insecure file inclusion
Some PHP applications construct file paths from user-controlled values. If these values are not safely restricted, an attacker may cause the application to access unintended files or, under particular conditions, execute code.
Prevention: Avoid using raw user input to select files. Use fixed allowlists of permitted templates and resources.
6. Broken access controls
A user may be able to access another member’s private content or administrative features if the application checks only whether someone is logged in rather than whether they are authorized to perform a specific action.
Prevention: Check permissions on the server for every sensitive request. Do not rely on hidden buttons or interface restrictions.
7. Session and authentication weaknesses
Weak session handling can increase the risk of account impersonation. Poor password-reset procedures, exposed session tokens, and missing protections for administrator accounts can also create security gaps.
Prevention: Use secure session cookies, regenerate session identifiers when appropriate, implement multi-factor authentication for privileged accounts, and invalidate sessions after sensitive account changes.
8. Outdated PHP versions and dependencies
Unsupported PHP versions may no longer receive security fixes. Outdated frameworks, plugins, and libraries can also expose applications to known vulnerabilities.
Prevention: Maintain a software inventory, track vendor advisories, remove unused dependencies, and update software according to a tested patch-management process. PHP publishes its branch support and end-of-life information on its official website.
Warning Signs of a Potentially Hacked PHP Website
A compromised website does not always show obvious symptoms. Some attacks are designed to remain unnoticed, while normal technical problems can resemble security incidents.
Investigate the following warning signs:
Unexpected administrator accounts: New privileged accounts appear without an authorized explanation.
Unfamiliar file changes: PHP files, configuration files, or scheduled tasks change unexpectedly.
Unusual server activity: CPU usage, outgoing traffic, or request volumes rise sharply without a clear business reason.
Unexpected redirects: Visitors are sent to unfamiliar pages, advertisements, or suspicious domains.
Unusual login activity: Repeated failed logins, unfamiliar administrator sessions, or unexpected password-reset requests appear in logs.
Database anomalies: Records change unexpectedly or new accounts and content appear without authorization.
Security alerts: Hosting providers, malware scanners, or monitoring tools flag suspicious activity.
None of these signs proves a hack on its own. Check timestamps, deployment records, application logs, and hosting alerts to determine what happened.
If you suspect a compromise, preserve relevant logs and evidence before making changes that could erase useful information.
How to Secure a PHP-Powered Social Media Website
Use this practical checklist to strengthen web application security. Adapt each control to your architecture and risk level.
hese are practical starting intervals, not universal compliance rules. Internet-facing systems and high-risk applications may need more frequent reviews.
Common PHP Website Security Mistakes
Website owners often leave avoidable gaps even when they understand the importance of security.
Ignoring outdated software: An old PHP branch or abandoned plugin may no longer receive necessary fixes.
Trusting file extensions alone: A filename does not prove that an upload contains safe content.
Giving excessive permissions: An application process with unnecessary privileges can increase the impact of a compromise.
Storing secrets in source code: Exposed repository credentials can provide access beyond the original application.
Checking permissions only in the interface: Hiding an administrative button does not prevent direct unauthorized requests.
Keeping untested backups: Backups that cannot be restored—or contain compromised files—may fail during an emergency.
Ignoring suspicious activity: Unexplained redirects, file changes, or login events deserve investigation.
Assuming an update solves everything: Patching a vulnerability does not automatically remove malware or reverse unauthorized access that occurred earlier.
Key Takeaways
PHP vulnerabilities in social media websites can affect accounts, private data, media uploads, and server operations.
Critical PHP security advisories published on October 21, 2026, identify two remote-code-execution vulnerabilities requiring prompt remediation.
PHP+1SQL injection, XSS, insecure uploads, broken access controls, and outdated dependencies remain important areas for defensive attention.
Strong security combines patching, secure coding, restricted permissions, monitoring, and tested backups.
If a website is compromised, investigate the root cause and scope instead of relying on superficial cleanup.